Introduction
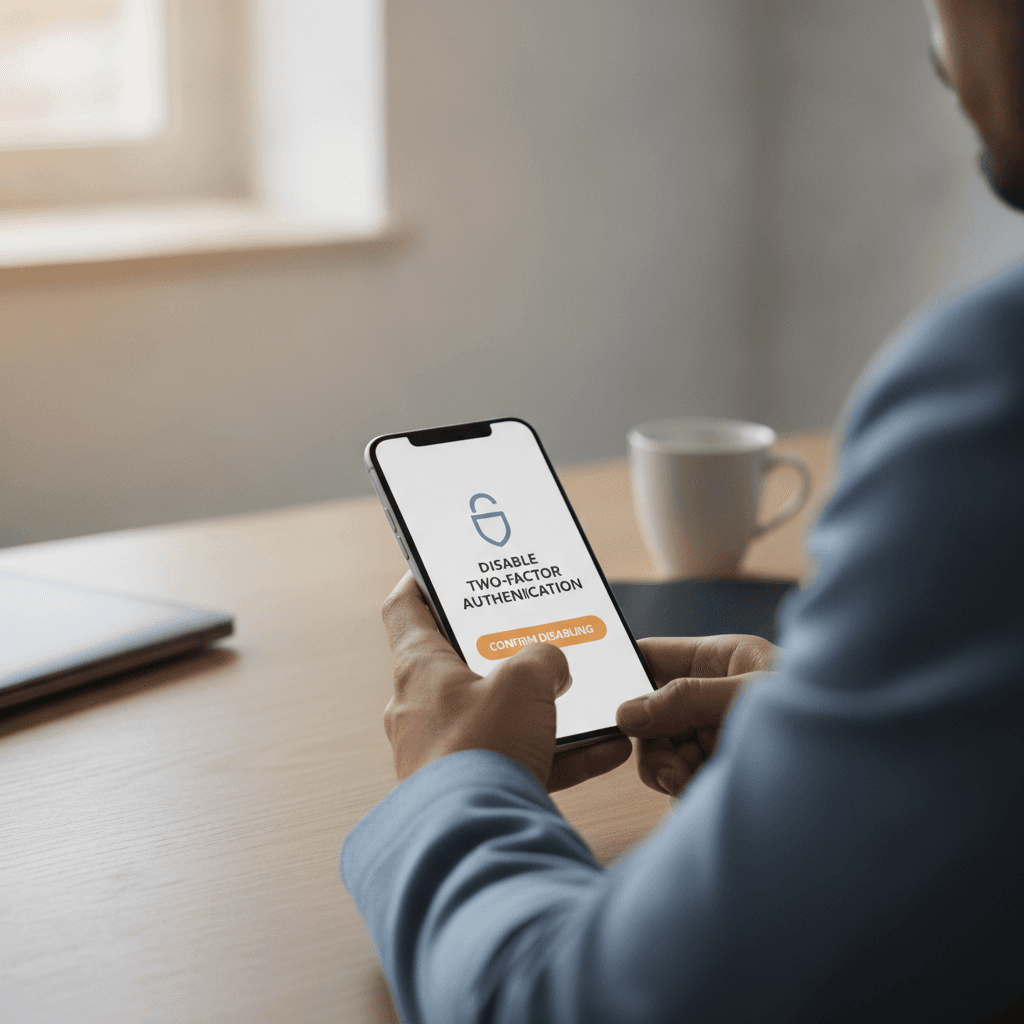
When you need to disable two-factor authentication, you're making a deliberate choice to remove a critical security layer from your accounts. Two-factor authentication (2FA) is a security feature that requires users to verify their identity through two separate methods before accessing their accounts—typically a password plus a code sent to your phone or generated by an authenticator app. While this extra layer of protection significantly reduces the risk of unauthorized access, there are situations where you may need to turn off two-factor authentication — whether temporarily for troubleshooting, permanently due to device loss, or to accommodate specific workflow requirements.
Understanding when and how to safely disable two-factor authentication requires balancing security concerns with practical access needs. Many users find themselves locked out of accounts when they lose access to their authentication device, while others need to disable 2FA to integrate third-party applications or manage shared accounts. The process of turning off this security feature varies significantly across platforms, and making the wrong choice can leave your account vulnerable to identity theft and unauthorized access.
Financial institutions face particular challenges in this area. Federal regulations require reasonable policies and procedures to protect account holders from identity theft, which often includes guidelines for authentication management. When you need to dispute credit report errors or resolve account access issues, understanding your options for managing two-factor authentication becomes critical to maintaining both security and accessibility.
The decision to disable 2FA should never be taken lightly. Each platform implements authentication differently, and the implications of turning off this protection vary based on the sensitivity of the data involved, the availability of alternative security features, and your specific use case. This guide walks you through the considerations, procedures, and best practices for safely turning off two-factor authentication when circumstances require it.
Why You Might Need to Disable Two-Factor Authentication
Two-factor authentication adds a layer of security to your accounts, but it doesn't come without friction. When you're locked out of your authenticator app, switching phones, or dealing with a lost device, that extra security step transforms from protection into an obstacle. The very mechanism designed to keep you safe can become the barrier preventing you from accessing your own accounts.
The problem intensifies when you need immediate access. A time-sensitive transaction, an urgent password reset, or a critical account change doesn't pause while you hunt for backup codes or wait for SMS delivery. Financial institutions and service providers have built increasingly complex verification requirements, and while these protect against unauthorized access, they can also trap legitimate account holders in verification loops.
Common Two-Factor Authentication Roadblocks
Device changes create the most frequent disruption. When you upgrade your phone or replace a broken device, authenticator apps don't automatically transfer. You're left holding a new device that can't generate the codes your accounts expect, while your old device—with all those configured accounts—sits inaccessible or wiped clean.
Phishing attempts add another layer of complexity. Receiving an email or text from what appears to be your bank asking you to verify account information could indicate a phishing attempt, making users wary of legitimate verification requests. This confusion between real security measures and fraudulent ones leaves many people uncertain about when to engage with two-factor prompts and when to ignore them.
Backup codes present their own challenge. Most platforms generate a set of one-time recovery codes when you enable two-factor authentication, but few users store them securely or remember where they saved them months later. Without these codes, legitimate account recovery becomes a manual verification process that can take days.
The authentication burden multiplies across accounts. Managing two-factor settings for email, banking, social media, work systems, and cloud storage means maintaining multiple authenticator entries, multiple backup code sets, and multiple recovery procedures. When one piece of this system breaks, the cascade can lock you out of interconnected accounts that rely on each other for recovery. If you're managing multiple security settings across platforms, you might also benefit from learning how to automate your savings to reduce the number of manual account interactions you need.
The security measure that protects your account can become the lock that keeps you out when verification methods fail or devices change.
Some situations demand temporarily turning off two-factor authentication: troubleshooting account access issues, consolidating authentication methods, or preparing for extended periods without reliable phone service. Understanding when and how to safely disable these protections—and when to keep them active despite the inconvenience—requires balancing security needs against practical access requirements.
How to Disable Two-Factor Authentication: Step-by-Step Guide
Disabling two-factor authentication requires a deliberate, platform-specific approach. Most services place the setting inside account security menus, but the exact path varies. The steps below outline the general process and highlight where major platforms differ.
General Process Across Platforms
Most platforms follow a similar pattern. Log in to your account using your current credentials, including the second factor if it's still active. Navigate to account settings—usually under a profile icon or menu in the top corner. Look for a security or privacy section. Inside, you'll find two-factor authentication listed alongside password and recovery options.
Once you locate the 2FA setting, the platform will ask you to confirm your identity. This might mean entering your password again, providing a code from your authenticator app, or answering a security question. After confirmation, you'll see an option to turn off or disable 2FA. Select it, confirm the action, and the platform will remove the second factor from your login process.
Platform-Specific Variations
Some platforms add extra steps or place the setting in less obvious locations. Email providers often nest 2FA under "Account Security" or "Sign-In & Security." Social media platforms may label it "Login Approval" or "Two-Step Verification." Financial services and enterprise tools sometimes require you to contact support or complete a waiting period before the change takes effect.
If you're managing 2FA for a service that enforces it at the organizational level, you may not have permission to disable it yourself. In that case, reach out to your administrator or IT team.
What Happens After You Disable It
Once disabled, your account reverts to single-factor authentication—password only. You'll no longer be prompted for a code at login. Any authenticator app entries or SMS numbers linked to the account remain in your records, but the platform won't use them. If you decide to re-enable 2FA later, you'll need to set it up again from scratch, including generating new backup codes.
If you're disabling 2FA temporarily—say, to switch devices or troubleshoot an issue—plan to turn it back on as soon as the task is complete. For more on managing account security during transitions, see How to Dispute Credit Report Errors: A Step-by-Step Guide for a parallel example of navigating identity verification steps.
Disabling two-factor authentication is straightforward once you know where to look, but the real decision is whether the convenience is worth the risk.
Security Best Practices After You Disable Two-Factor Authentication
Disabling two-factor authentication doesn't mean abandoning security altogether. The moment you turn off that second layer of protection, you're relying entirely on your password — and that password needs to carry the full weight of keeping your account safe. Think of it as removing the deadbolt from your front door: the knob lock better be solid.
Strengthen Your Primary Password
Your password is now your only defense. Make it count. Use a unique, complex passphrase for each account — at least 12 characters mixing letters, numbers, and symbols. Never reuse passwords across platforms; if one service is breached, attackers will try that same credential everywhere else. A password manager can generate and store strong passwords without forcing you to memorize random strings.
Monitor Account Activity Closely
Without two-factor authentication, unusual login attempts won't trigger a secondary challenge — they'll just succeed if the password is correct. Review your account's login history weekly. Most platforms show recent sessions, IP addresses, and device types. If you spot an unfamiliar location or device, change your password immediately and investigate whether any account settings were altered.
Enable email or SMS alerts for login events if your platform offers them. These notifications won't block unauthorized access the way two-factor authentication does, but they'll tell you when someone gets in, giving you a narrow window to respond before damage occurs.
Use Platform-Specific Security Features
Many services offer security controls beyond two-factor authentication. Device recognition flags logins from new hardware. Trusted IP ranges restrict access to known networks. Session timeouts force re-authentication after inactivity. Review your account's security settings and activate every feature that fits your workflow — they won't replace two-factor authentication's strength, but layered controls raise the effort required to compromise your account.
If you're managing multiple accounts without two-factor authentication, consider whether you need all of them active. Dormant accounts are attractive targets; attackers probe old credentials hoping you've forgotten to secure them. Close accounts you no longer use, or at minimum, update their passwords and check for lingering linked services. For more on trimming unnecessary digital overhead, see our guide on how to cancel subscriptions that save you $1,800 a year.
Plan for Re-Enabling Two-Factor Authentication
Disabling two-factor authentication should rarely be permanent. Once you've resolved the immediate need — whether that's replacing a lost phone, switching authenticator apps, or completing a system migration — turn it back on. Document your backup codes in a secure location (not your email inbox) and verify that your recovery contact information is current. If the platform supports hardware security keys, consider adding one as a fallback method that doesn't depend on a phone or app.
Regular security reviews keep you ahead of threats. Schedule a quarterly check to confirm two-factor authentication is active on critical accounts, update recovery methods, and audit which devices have active sessions. Treating security as an ongoing process, rather than a one-time setup, ensures you're not caught off guard when the next credential breach makes headlines.
Conclusion
Disabling two-factor authentication is sometimes necessary — whether you're troubleshooting login issues, switching devices, or dealing with lost access to your authenticator app. The steps outlined in this guide give you a clear path to turn off 2FA across major platforms without getting locked out or leaving your account exposed during the transition.
But disabling 2FA doesn't mean abandoning security altogether. The moment you turn off that second layer of verification, your account becomes more vulnerable to unauthorized access. If you've disabled 2FA temporarily, set a calendar reminder to re-enable it as soon as the underlying issue is resolved. If you've turned it off permanently, compensate by using a strong, unique password and enabling login alerts so you're notified immediately if someone tries to access your account from an unfamiliar device.
Financial institutions and creditors are required to maintain reasonable policies and procedures to identify risks to account holders, including those related to identity theft. While these guidelines focus on institutional safeguards, they underscore a broader principle: layered security isn't optional in a world where credential breaches happen daily. Your personal accounts deserve the same vigilance.
If you're managing multiple accounts and struggling to keep track of security settings, consider using a password manager that can also store backup codes and track which accounts have 2FA enabled. This creates a single source of truth for your authentication setup and makes it easier to audit your security posture regularly. For more guidance on protecting your financial accounts and personal data, see our guide on how to dispute credit report errors — another area where proactive monitoring can prevent larger problems down the line.
Ultimately, disabling two-factor authentication should be a deliberate decision, not a default. Use it when you need to, secure your account during the gap, and get that second factor back in place as soon as you can. Your future self — the one who doesn't have to recover a compromised account — will thank you.
FAQ
What happens when I disable two-factor authentication?
When you disable two-factor authentication, your account reverts to password-only protection. You'll no longer be prompted for a second verification code at login, and any linked authenticator apps or SMS numbers will stop being used for verification.
Can I temporarily disable two-factor authentication?
Yes, you can disable two-factor authentication temporarily and re-enable it later. However, you'll need to set it up again from scratch, including generating new backup codes and reconfiguring your authenticator app.
Is it safe to disable two-factor authentication?
Disabling two-factor authentication significantly reduces your account security. If you must disable it, use a strong unique password, enable login alerts, and plan to re-enable 2FA as soon as possible.
How do I disable two-factor authentication if I lost my phone?
If you've lost your phone, use backup codes if you saved them, or contact the platform's support team for account recovery. Most services have a manual verification process for users who've lost access to their authentication device.
Learn how to disable two-factor authentication when you need to with this straightforward guide.
Related reading
Discord 2FA Management: How to Disable Two-Factor Authentication